
As previously reported on 3D Printing Industry, the protection of intellectual property (IP) in CAD files is a chief concern, not only for independent designers, but for companies seeking security over digital assets.
As a solution to design theft, a research team at the New York University Tandon School of Engineering, propose a security feature for CAD files to make them fail if 3D printed incorrectly.
We reported last year on research that introduced flaws into a 3D print for malicious purposes, however this latest paper aims to use the flaws in a 3D print for good, rather than evil.
Imperfections enter stealth mode
In this proof-of-concept study, researchers hypothesise a security feature within CAD software that deliberately inserts faults into a component’s design. If 3D printed with the correct settings, the object will keep the desired quality. However, if the .stl file is not processed with the correct settings, the object will 3D print with a critical imperfection.
To test this hypothesis, the researchers examine two file modifications for creating unnoticeable flaws.
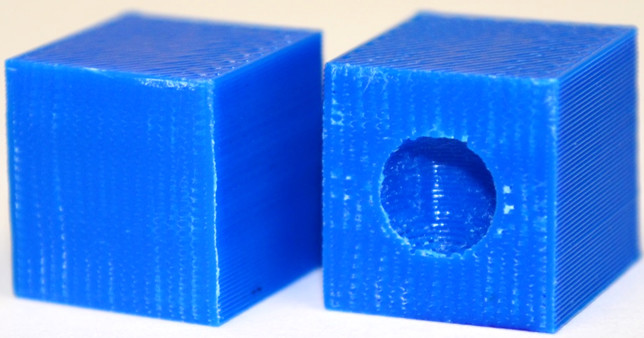
In the first instance the team investigate a command to create a split within a part. With this command, CAD engineers can embed a curved surface inside the geometry of a part. As this surface should not be present in a solid object, the curve creates a fracture in the demonstrated bar, making it unusable for the purpose.

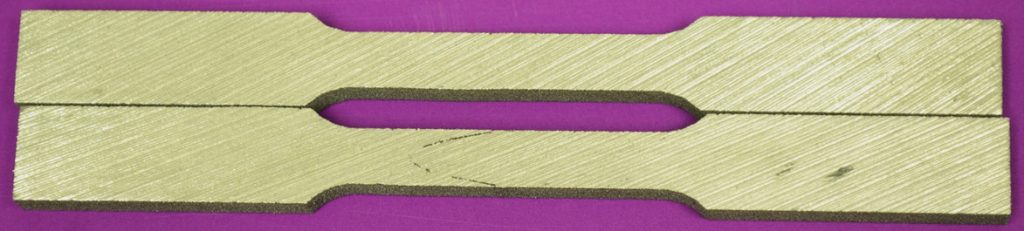
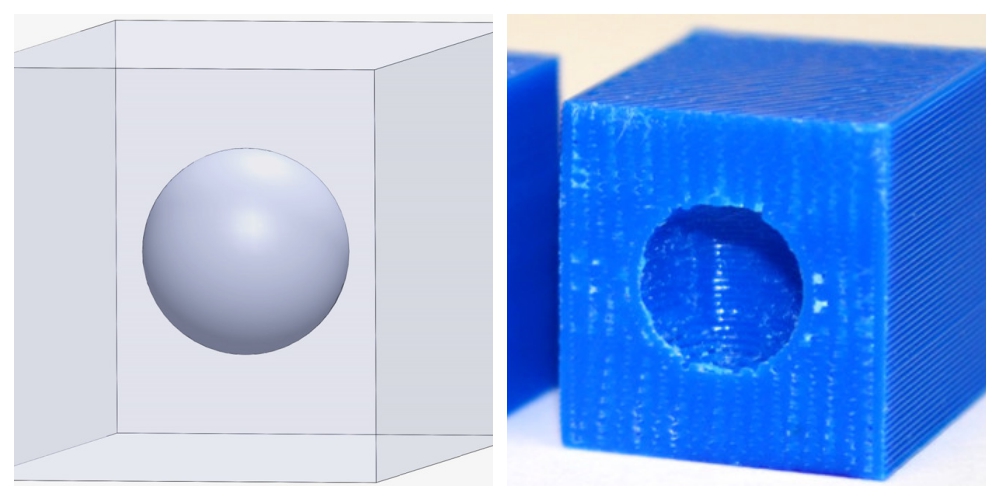
Second, the researchers embed a sphere into the internal geometry of a cube. When sliced with the incorrect parameters, the 3D printer is programmed to believe it is making a solid cube, but following the 3D shape it encounters the sphere, leaving a cavity in the surface.
Simple but effective
Though the examples shown are simple shapes, the flaw concept is easily transferable to more complex parts. The particular type of flaw must also be considered on a part by part basis, as it is dependent upon a part’s dimensions and the internal geometry.
Fei Chen, one of the co-authors on the study, comments
The range of security feature designs demonstrated in this work can provide great flexibility to application engineers in terms of how to disguise these flaws easily in a complex shaped part. Most industrial components manufactured using 3D printing have complex designs to justify the use of 3D printing, which further helps in embedding these features without detection.
It is also worth noting that, although the imperfections could be removed by an experienced CAD user, multiple flaws in a complex part would be laborious to fix.
Nikhil Gupta, lead author of the Tandon School of Engineering study, adds,
…cybersecurity tools can be applied as usual to make the files and cloud secure; however, in case the design files are stolen, there is nothing in the designs to deter printing a high-quality component. The new approach is designed to provide an advantage in this scenario and to make printing high-quality parts from stolen files difficult.
Protection for 3D printing
With the additive manufacturing market becoming more and more competitive, some 3D printing companies are taking steps to patent features and processes in their work. IP protection for digital designs has also been discussed in relation to a copyright case between cheerleading uniform producers Varsity Brands and Star Athletica.
Tandon School of Engineering’s full article on this study, titled Security features embedded in computer aided design (CAD) solid models for additive manufacturing, is published online in the journal Materials & Design, Volume 128. It is co-authored by Fei Chen, Gary Mac and Nikhil Gupta. You can read an interview with Professor Gupta by 3D Printing Industry editor-in-chief Michael Petch here.
For more of the latest 3D printed related research, sign up to the 3D Printing Industry newsletter, like us on Facebook and follow us on Twitter.
Featured images: CAD model of a 3D printable cube with embedded flaw (sphere). Image credit Nikhil Gupta, Ph.D.

=/ now how does one export an stl that is printable on multiple machines with any slicer. this “encryption” method has NO cross platform capability.
That’s stupid. Now designers can’t protect their stl files we might as well not even make the stl available in the first place. The only person who will be able to steal it is the printing bureau and they already have the stl file and working slicer.
For instance a user can tell you their machine, slicer and material. You then synthesize an STL and a set of slicing parameters.
The print will fail if a third party attempts to naively print the STL using different build parameters, machine, or material. To print the object successfully, the third party will have to intercept the part’s metadata – the slicing parameters and machine/material target.
This is security by obscurity, however. If the third party creates an algorithm that automatically reverse engineers the part, then there is no benefit. And I somewhat down that the difficulty of building such an algorithm is guaranteed mathematically, as in other cryptographic security protocols.
This is not helpful. What happens when I want to code once and deploy many places. I do this with my software. I cannot do this with my models that I print on either a makerbot, EOS metal printers, or other FormLABs SLA machines as each vendor uses a different slicer and new slicers are always being made and improved upon. I export one 1 highest resolution STL. I’m not going to waste additional cpu time on extra versions of my model for every printer. That should be the slicer’s responsibility software & ecosystem – wise — to parse an stl to g-code print instructions given a printer it connects to/supports. Furthermore, the future of engineering high quality models is in parametric nurbs modelling — something like solidworks that runs a nurbs kernel like rhino, saving your surfaces and curves as actual math and not polygonal approximations. You can reverse engineer any open source slicer which will be the most popular solution for hackers as most slicers are open source and non-proprietary.
Viktor Jondal James Mcarthur maybe we should reach out to them
Sell your prints, not your files.